ISAE 3402 Type II confirms that our IT processes function effectively. Your data is safe with our reliable security measures.
The statement
An independent auditor tests whether the controls actually work.
Type II
Type II tests not just the design, but the operation over a period.
For customers
Fewer checks of your own needed during audits and tenders.
This year, we have once again successfully obtained the ISAE 3402 Type II Assurance Report. This independent audit confirms that our internal processes are both well-structured and function effectively when it comes to information security.
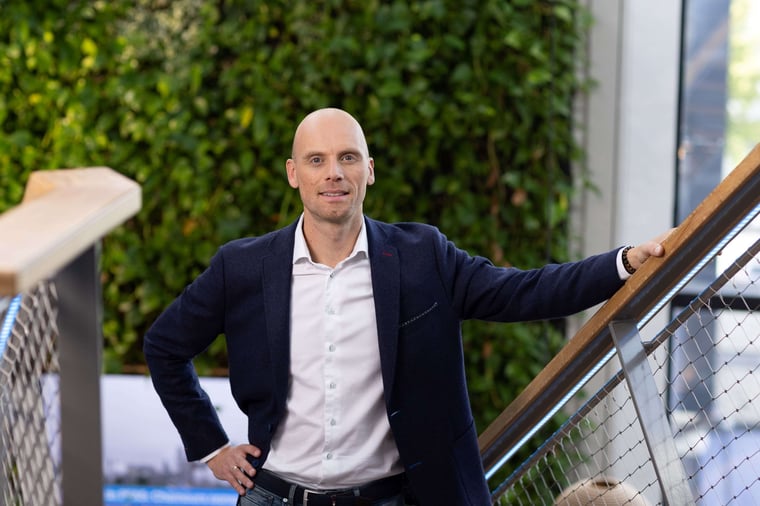
"The renewed award of the ISAE 3402 Type II report shows that our processes are not only correct on paper, but also demonstrably effective," says Edward Bakker, Security Officer at ISPnext.
What does this mean?
ISAE 3402 Type II is an international standard that confirms that an organisation has its IT and security measures structurally in order. In our case, this applies to the development and hosting of the Source-to-Pay platform on Microsoft Azure. "The audit focuses on how we manage our processes, particularly in the areas of development, infrastructure and compliance," Edward said.The audit focused on, among other things:
Development & testing
Secure software development processes, including testing procedures
Infrastructure
Hosting via Azure, including backups and recovery
Security & privacy
Compliance with the AVG and other laws and regulations
Logging & monitoring
Continuous supervision of our systems and critical processes
5 tips for a successful Source-to-Pay implementation
Discover what to watch out for in a Source-to-Pay implementation.
Why this is relevant
For customers, this report mainly means more certainty. It shows that we handle data carefully and comply with relevant laws and regulations. It also reinforces confidence in audits or due diligence processes. "For clients, this report confirms that we have a grip on our processes and handle their data with care," says Edward Bakker.
Growth, standardisation and trust
At ISPnext, we pride ourselves on our continued growth and progress. Our strategic focus is on international expansion that is both strong and scalable. By standardising our internal processes and working to proven best practices, we are able to offer our customers significant operational and financial benefits. "This standardisation ensures that we can continue to grow without compromising on quality and safety," concludes Edward.
“For customers, this report confirms that we have a grip on our processes and handle their data with care.”
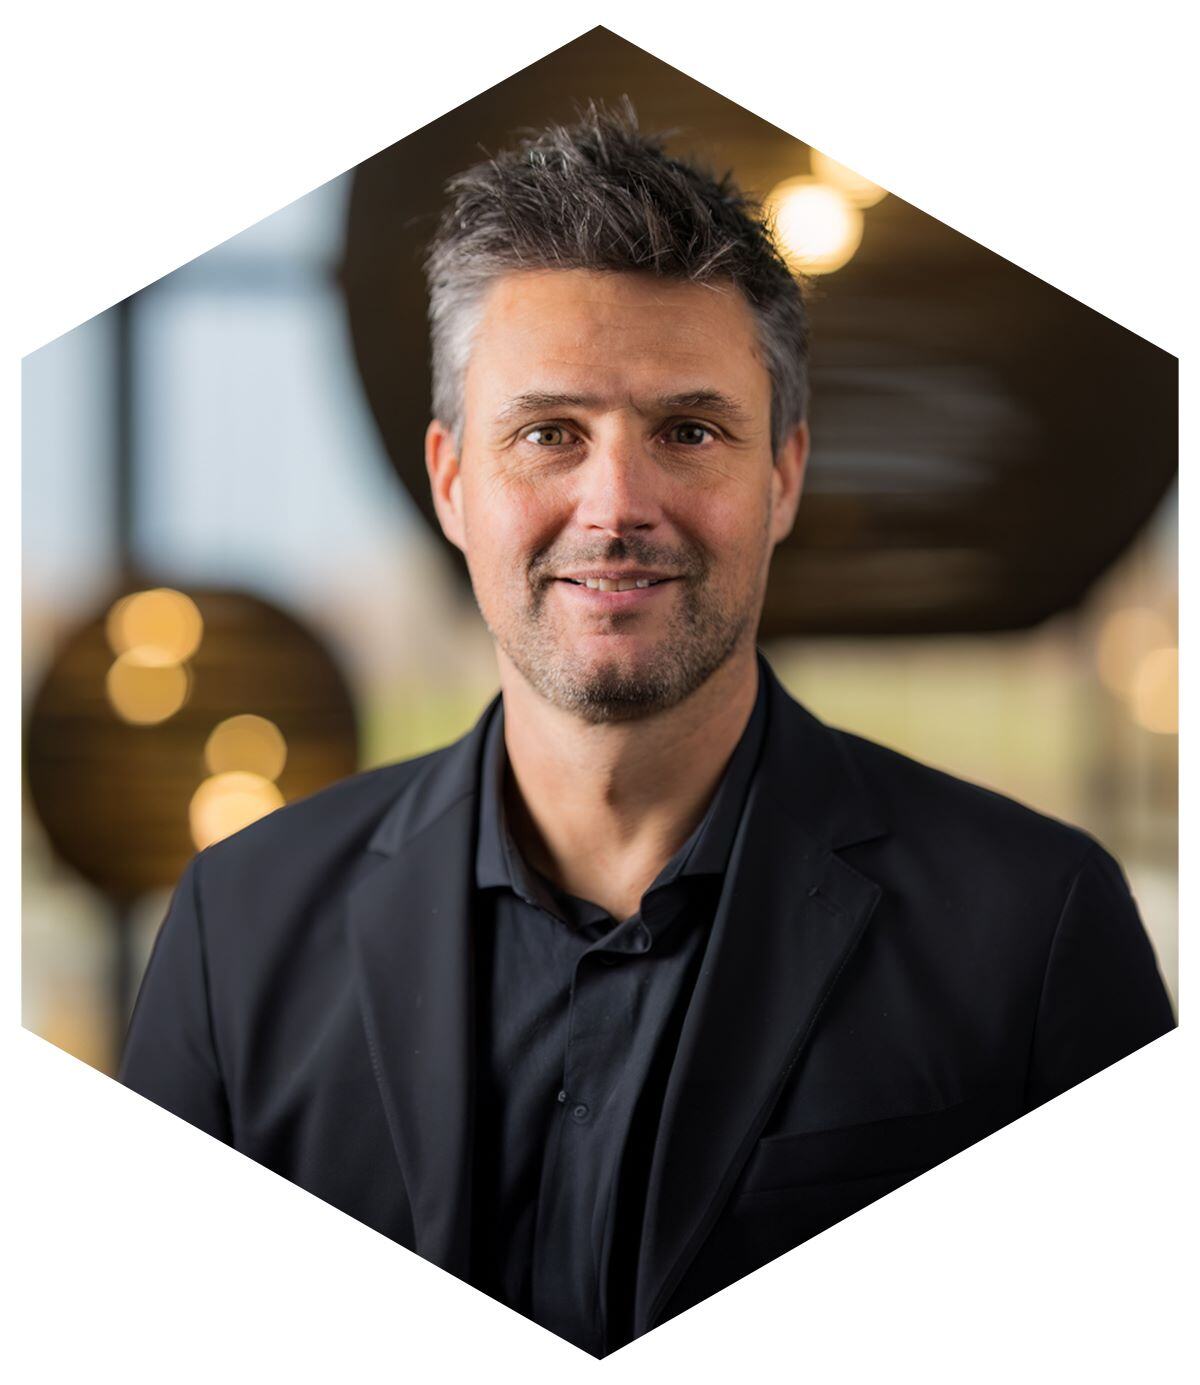 Edward BakkerSecurity Officer | ISPnext
Questions?
Do you have questions about our ISAE3402 Type II Assurance Report or are you curious about our security measures? Feel free to contact our Security Officer. For existing customers, our Sales Team and Customer Success Team are also ready to help.
Frequently asked questions
ISAE 3402 has two variants. Type I assesses whether internal controls were properly designed at a particular point in time. Type II goes a step further: it also looks at whether these controls have worked well in practice over a longer period of time.
Originally, the focus of ISAE 3402 was on financial processes, but its application is much broader nowadays. In our case, for example, the report also covers IT-related processes such as software development, hosting, data security and systems monitoring.
Although these standards have common ground, they focus on different aspects. ISAE 3402 mainly looks at internal control measures within outsourced processes. ISO 27001 focuses more on general policies around information security. SOC 2, on the other hand, evaluates the reliability of IT services, especially in the context of the US market.
Such a report is issued annually, following a thorough audit by an independent party. This examines whether our controls worked well throughout the previous year. That way, we stay focused on improvement and maintain transparency to our customers.