Digital resilience with DORA
Digital threats are becoming more frequent, more complex and more damaging. With the introduction of the Digital Operational Resilience Act (DORA), financial institutions and their IT service providers face a clear obligation: making sure their digital infrastructure is robust, traceable and fully compliant.
- What the DORA regulation actually involves
- Who the regulation applies to
- How to achieve compliance
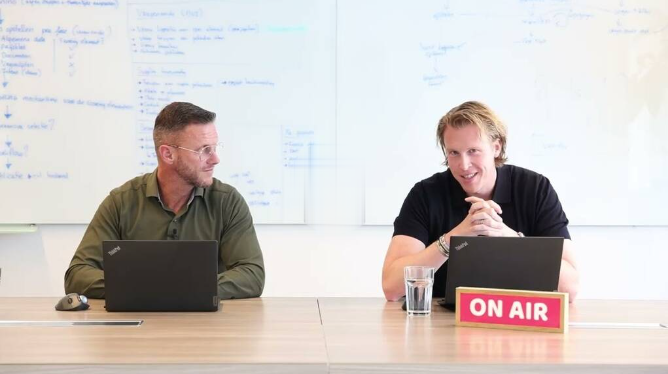
Control over risk, continuity and IT contracts
This regulation changes how organisations manage risk, continuity and the oversight of IT services delivered by third parties. You'll discover how Contract Management and Vendor Management help you gain visibility into your ICT suppliers and keep DORA compliance demonstrable.
What can you expect
What the DORA regulation actually involves and why it matters right now.
Who the regulation applies to, from financial institutions to their ICT suppliers.
How to achieve compliance and demonstrate it to regulators.
Which processes and technologies can support your compliance journey.
Who you'll hear from
Product Manager at ISPnext, specialised in contract management and supplier risk management.
Solution Consultant at ISPnext, showing how organisations gain control over suppliers and compliance.
Built for compliance & risk teams
Manage the risk of your ICT suppliers and demonstrate compliance with DORA.
Link contracts to DORA requirements and keep suppliers clearly in view.
Work with IT and procurement to build a DORA-ready supplier chain.
Frequently asked questions about DORA
What exactly is DORA?
DORA stands for the Digital Operational Resilience Act. It's European legislation that requires organisations to strengthen their digital resilience, meaning better preparedness for ICT risks, cyber incidents and IT service outages.
Why does DORA matter for my organisation?
DORA has been in force since January 2025 and applies to all financial institutions and their ICT service providers. It requires organisations to properly set up risk management, incident management and contract management with ICT suppliers. Without this in place, you risk sanctions or reputational damage.
What will I learn in this webinar about DORA?
In the webinar you'll discover the key obligations, how to make ICT contracts visible and keep them compliant, and how ISPnext can help with supplier risk management and contract management. You'll also get practical steps to make your organisation DORA-ready.
Who is this webinar for?
The webinar is for anyone responsible for ICT or supplier contracts, compliance, audit, risk management, finance, IT or procurement.
What is ISPnext's role in DORA compliance?
ISPnext helps organisations manage contracts, suppliers and risk through one digital platform, letting you assess ICT suppliers for risk, link contracts to DORA requirements and easily report on compliance.
Is the webinar free and how long does it take?
Participation in the webinar is free. It takes about thirty minutes and is available on-demand, so you can watch it whenever suits you.
Curious what DORA means for your organisation?
Schedule a demo and discover how ISPnext helps you with contract management, supplier risk and DORA compliance.